You've got to know how big your problem is before you build a plan to address it.

I run an independent advisory practice for regulated enterprises and the teams that build for them. Two decades governing vulnerability, audit, service management and technology risk at Fortune 50 scale, applied to your environment.

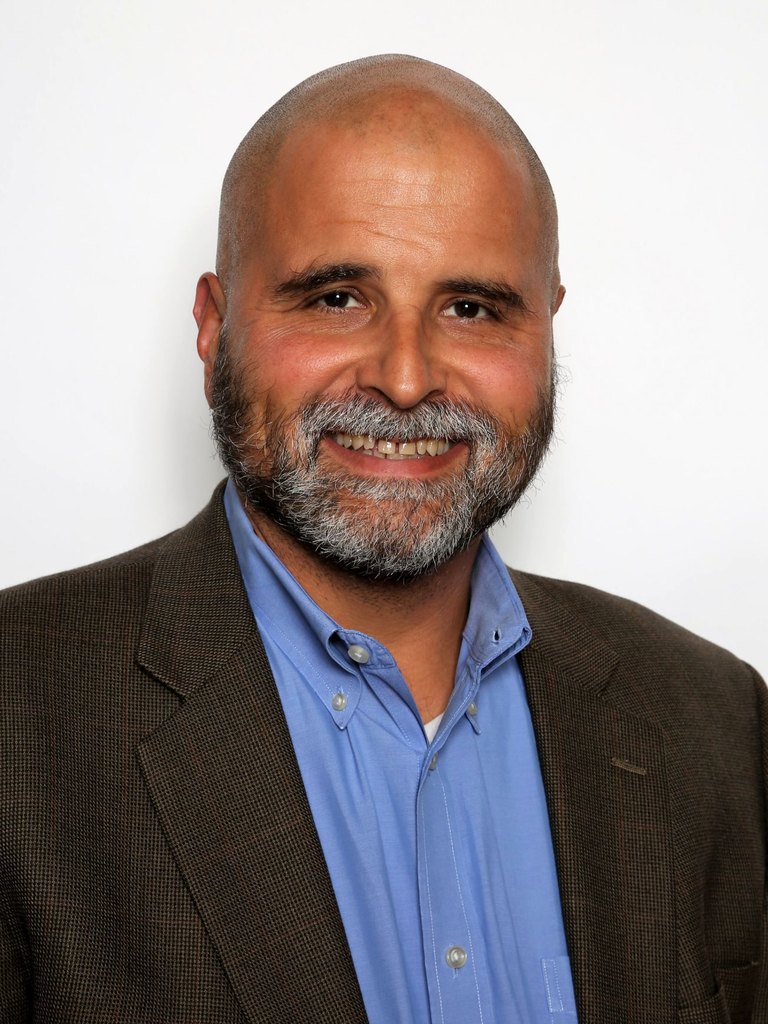
André Sanz
André SanzFounder & Principal
20+

Years leading technology risk in regulated enterprise

17

High-severity zero-day events driven to on-time closure

10,000+

Assets brought under enterprise vulnerability governance

0

Control failures across annual HIPAA and SOX audit cycles

Track record

Selected results.

  • At Evernorth Health Services (Cigna) — enterprise vulnerability governance established across 10,000+ assets; mean time to remediate critical findings down 18% in the first twelve months, critical backlog down more than 20%.
  • At Wells Fargo — emergency vulnerability response function built from nothing; 17 high-severity zero-day events closed on time, with zero regulatory escalations.
  • Across the HIPAA and SOX control environments at Evernorth — zero control failures in annual audit cycles, with centralized visibility for four business units.
  • At Wells Fargo — Incident, Problem, Change, Release and Knowledge Management governance for an infrastructure environment supporting more than 2,000 customers.
  • At GE Capital — release-related incidents reduced 50% through change governance redesign, across 10+ concurrent infrastructure and application releases.
  • At GE Capital — vendor on-time delivery across multi-client environments lifted from under 20% to more than 65%.

Capabilities

What I'm engaged to do.

Technology & Cyber Risk

Vulnerability, audit, and technology risk governed as one program, with reporting an executive committee can actually act on.

  • Enterprise Vulnerability Management
  • Emergency & Zero-Day Response
  • Audit & Regulatory Readiness
  • Risk Reporting & GRC Tooling
  • Security Hardening
Explore this practice

Service Management & Operations

Incident, problem, change and release governance, plus the delivery automation underneath, so a production estate stays predictable and can prove it to an auditor.

  • Incident & Problem Management
  • Change & Release Governance
  • Delivery & Infrastructure Automation
  • Service Delivery & SLA Management
  • Disaster Recovery & Operational Resilience
Explore this practice

Tell me what's breaking, what's slow, or what you're afraid to touch.

Every engagement starts with a conversation about outcomes, not hours. If I'm not the right fit, I'll be the first person to tell you.